Trust Center Reports
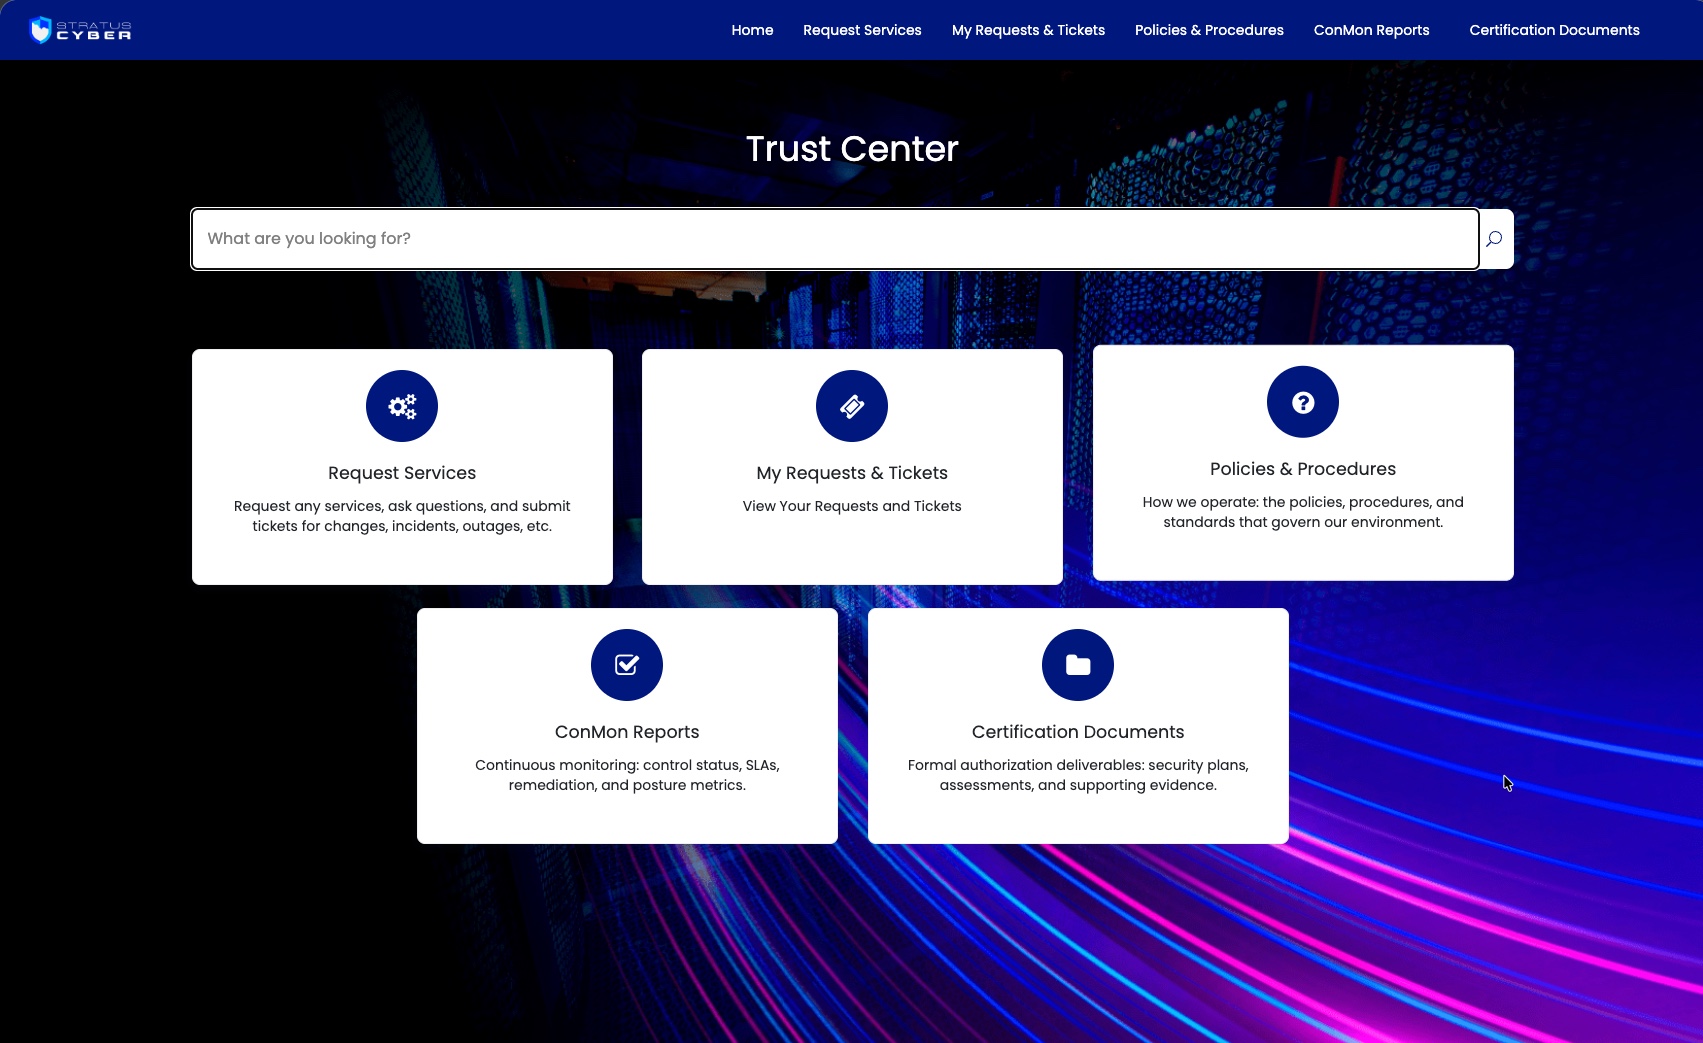
The Trust Center is the self-service portal through which agency and customer users reach their system's certification data. It carries five surfaces; the Trust Center Access Guide describes what each one serves.
Getting access
Request an account under User Access Requests in Request Services; the request is tracked as a Trust Center Access ticket. For how accounts are granted, the full tour of the surfaces, and programmatic access over the REST API, see the Trust Center Access Guide.
ConMon Reports
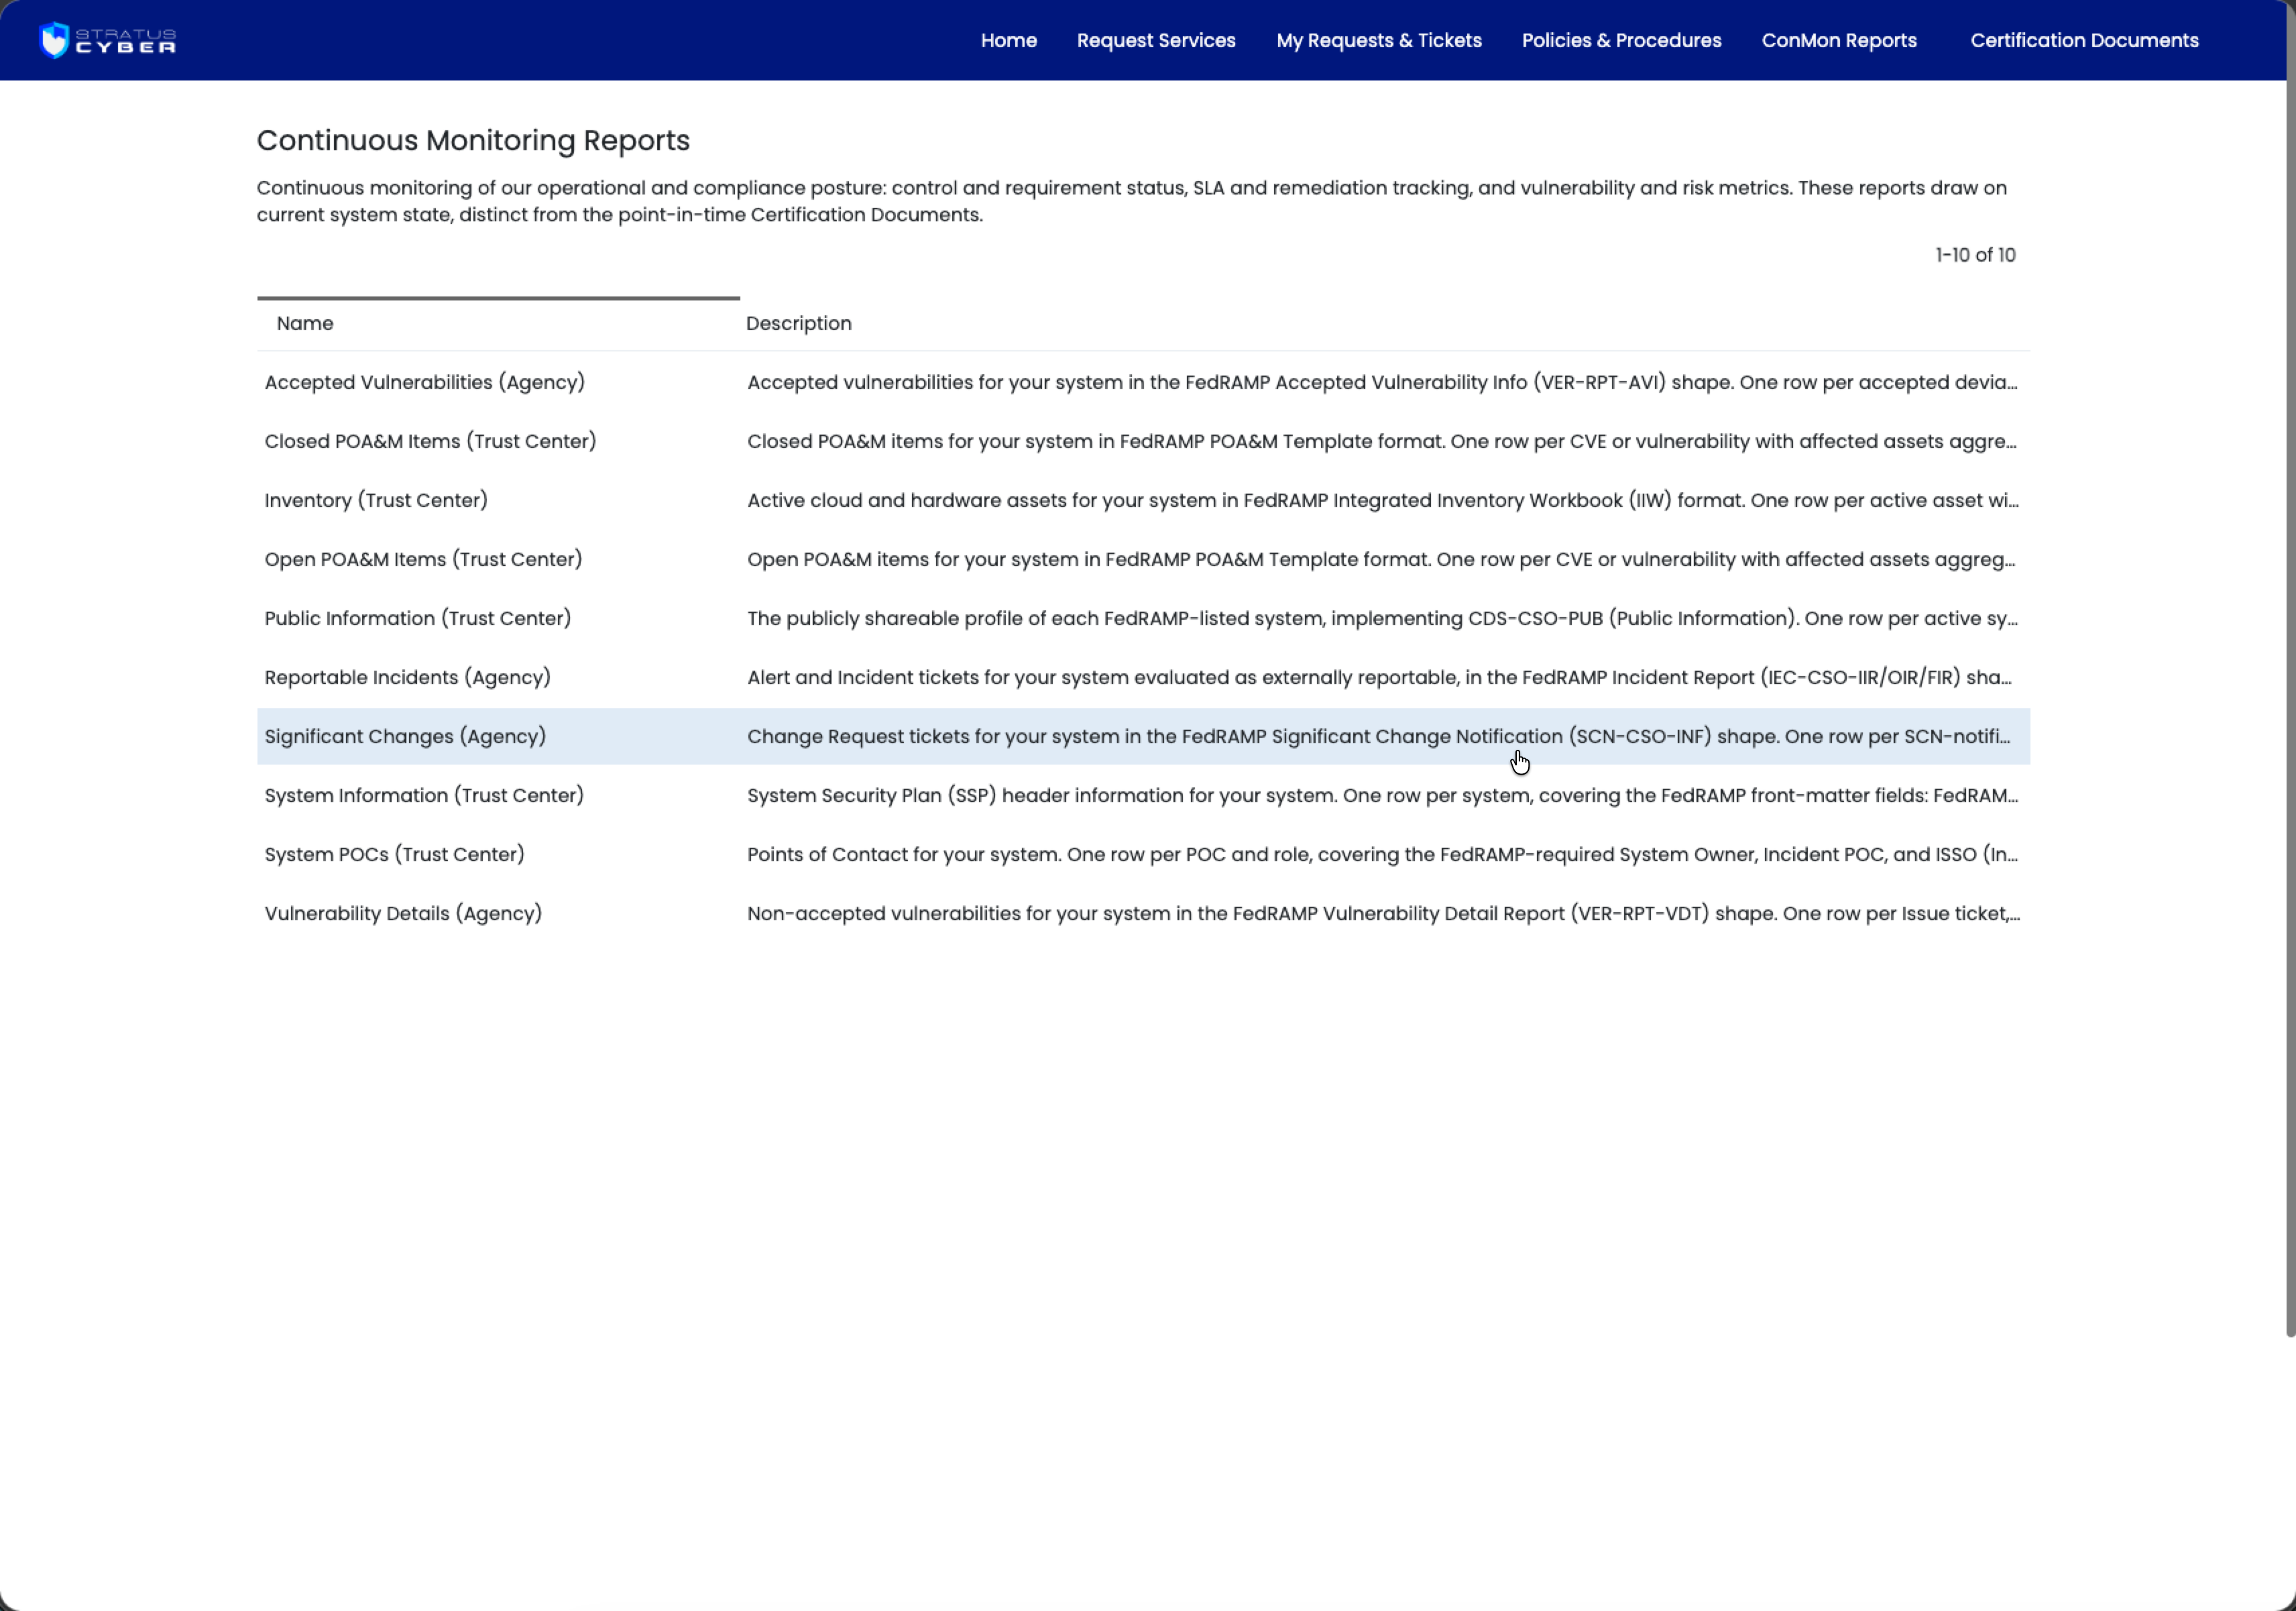
Ten reports, each in a FedRAMP shape, reading live system state. The Trust Center Access Guide holds the canonical list and explains live views versus fixed snapshots; the table below describes what each report contains.
| Report | What it contains |
|---|---|
| Public Information | The publicly shareable profile of each FedRAMP-listed system (CDS-CSO-PUB) |
| System Information | System Security Plan header information, covering the FedRAMP front-matter fields |
| System POCs | Points of Contact -- one row per POC and role, covering System Owner, Incident POC, and ISSO |
| Inventory | Active cloud and hardware assets in FedRAMP Integrated Inventory Workbook (IIW) format |
| Open POA&M Items | Open POA&M items in FedRAMP POA&M Template format, one row per CVE or vulnerability |
| Closed POA&M Items | Closed POA&M items in the same format |
| Vulnerability Details | Non-accepted vulnerabilities in the FedRAMP Vulnerability Detail Report (VER-RPT-VDT) shape |
| Accepted Vulnerabilities | Accepted vulnerabilities in the FedRAMP Accepted Vulnerability Info (VER-RPT-AVI) shape |
| Reportable Incidents | Alert and Incident tickets evaluated as externally reportable, in the FedRAMP Incident Report (IEC-CSO-IIR/OIR/FIR) shape |
| Significant Changes | Change Request tickets in the FedRAMP Significant Change Notification (SCN-CSO-INF) shape |
Reports are scoped to your own system: you see your system's records and nothing else, and sensitive fields are excluded from shared reports.
Policies & Procedures
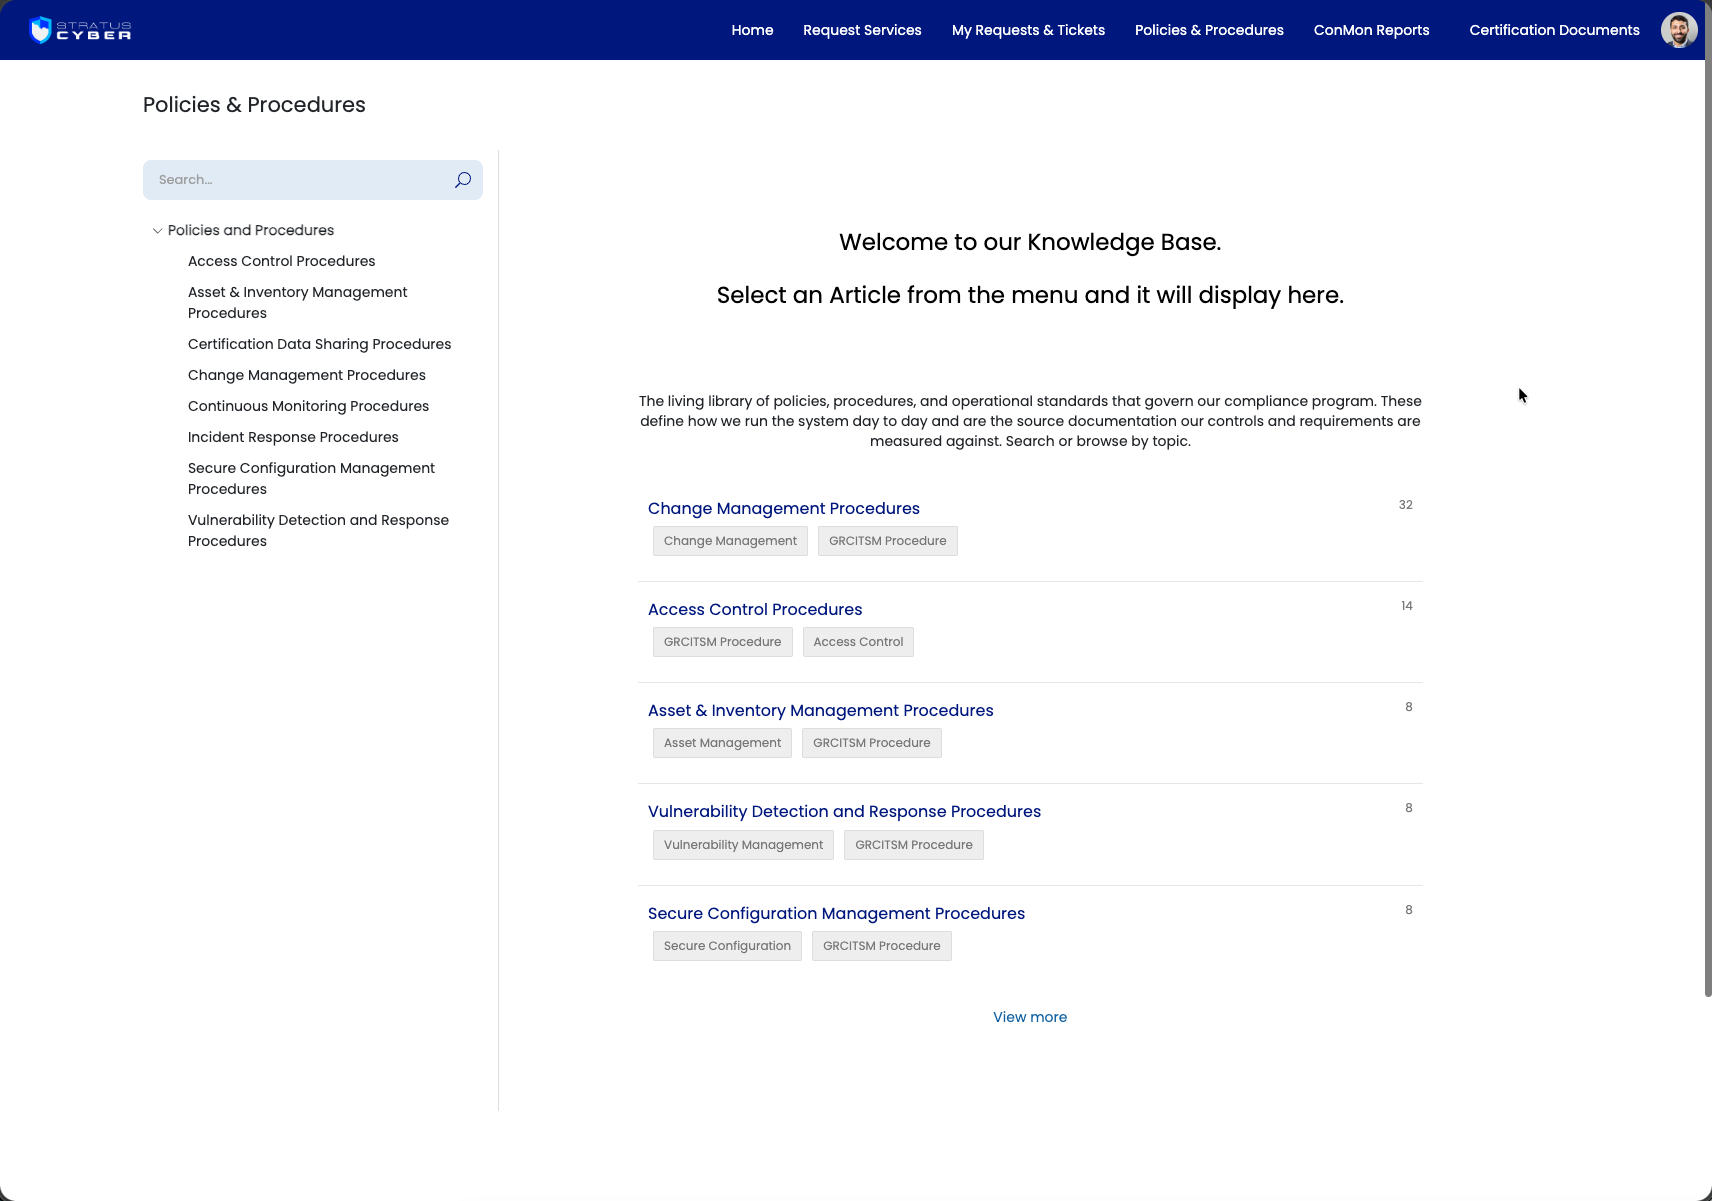
The published library of policy, procedure, and operational-standard articles the system's controls are measured against. Search or browse by topic; each article carries its topic tags.
Certification Documents
Point-in-time artifacts for the certification package, organized by system with folder selection. This includes the FedRAMP-schema JSON files (Security Decision Record, Certification Overview, Vulnerability Detail) plus uploaded package documents, with historical snapshots saved as each Ongoing Certification Report is issued.
Related documentation
- Trust Center Access Guide -- account access and the REST API
- Certification Data Sharing & Trust Center policy -- the policy behind these surfaces